{
"schemaVersion": 1,
"kind": "deterministic-regeneration",
"originalExecutionSourceCommit": "01166b4fe3c57475b45c5d533b8cd8003758e602",
"originalRunId": "6be5f6bb-df11-4567-96f9-70665751af7a",
"note": "No new model calls. Model outputs and usage are original; the final compiler corrects executable source provenance. Independent configuration checks are rerun; the historic model evaluator did not re-review new source.",
"regeneratedAt": "2026-10-15T10:50:20.487Z",
"run": {
"schemaVersion": 1,
"id": "6be5f6bb-df11-4567-96f9-70665751af7a",
"version": 9,
"mission": {
"ambition": "Make a useful, repeatable diagnostics system for this public Node repository.",
"beneficiary": "Maintainers and contributors who need reviewable checks they can own and extend.",
"outcome": "A source-grounded, runnable diagnostics package with a separate configuration review.",
"constraints": [
"Read only the named public repository.",
"Do not execute repository code, publish, deploy, contact people or claim passing diagnostics."
],
"acceptanceCriteria": [
"Every configured diagnostic exists in the inspected package.json.",
"The manifest identifies the exact inspected source revision.",
"The exported workflow grants only contents:read and uses the committed lockfile.",
"The review distinguishes configuration evidence from unexecuted repository diagnostics."
],
"repository": {
"owner": "unjs",
"name": "consola"
},
"budget": {
"maxModelCalls": 8,
"maxToolCalls": 2,
"maxOutputTokensPerCall": 4000
}
},
"status": "completed",
"tasks": [
{
"id": "investigate",
"dependsOn": [],
"status": "completed",
"attempts": 1,
"maxAttempts": 2,
"output": {
"summary": "The inspected source supports a repeatable diagnostics configuration centered on the existing `build`, `lint`, and `test` scripts, pnpm 10.6.3, and the committed `pnpm-lock.yaml`. No workflow or diagnostics manifest was supplied, so workflow permissions, lockfile-install usage, and revision-identification configuration cannot be verified from repository files. Repository diagnostics were not executed; this review makes no claim that they pass.",
"observations": [
{
"path": "package.json",
"evidence": "\"scripts\": {\n \"build\": \"unbuild\",\n \"dev\": \"vitest\",\n \"lint\": \"eslint . && prettier -c src examples test\",\n \"lint:fix\": \"eslint . --fix && prettier -w src examples test\",\n \"release\": \"pnpm test && pnpm build && changelogen --release --push && npm publish\",\n \"test\": \"pnpm lint && pnpm vitest run --coverage\"\n }",
"finding": "The package manifest defines the three requested diagnostics: `build`, `lint`, and `test`. The test script invokes linting before running Vitest with coverage; none of these commands was executed in this review."
},
{
"path": "package.json",
"evidence": "\"packageManager\": \"pnpm@10.6.3\"",
"finding": "The manifest pins the package-manager identity and version to pnpm 10.6.3, providing a source-grounded value for diagnostics setup."
},
{
"path": "package.json",
"evidence": "\"engines\": {\n \"node\": \"^14.18.0 || >=16.10.0\"\n }",
"finding": "The package declares supported Node.js engine ranges. A Node 22 diagnostics environment is compatible with the declared `>=16.10.0` alternative, but compatibility was not exercised."
},
{
"path": "pnpm-lock.yaml",
"evidence": "[Lockfile verified at immutable revision; 138945 bytes. Contents omitted by the evidence size limit.]",
"finding": "A committed pnpm lockfile is present in the inspected revision. Its contents were not available in the supplied evidence, so dependency resolution and lockfile consistency were not independently reviewed."
},
{
"path": "package.json",
"evidence": "\"release\": \"pnpm test && pnpm build && changelogen --release --push && npm publish\"",
"finding": "The manifest contains a release script with push and publish behavior. A diagnostics workflow should not invoke this script because it exceeds the mission's non-publishing and non-deployment constraints."
},
{
"path": "README.md",
"evidence": "",
"finding": "Coverage-reporting badge markup is commented out in the README. This is documentation configuration only and is not evidence that coverage reporting or upload is configured or has run."
}
],
"opportunities": [
{
"title": "Add a committed diagnostics manifest tied to the inspected revision",
"benefit": "Create a reviewable, non-executing manifest (for example, `diagnostics.json`) recording commit `c47faac1738b7383971c6c20b5a34ffa15e7cc3b`, package manager `pnpm@10.6.3`, Node 22, lockfile `pnpm-lock.yaml`, install command `pnpm install --frozen-lockfile --ignore-scripts`, and diagnostic commands `pnpm build`, `pnpm lint`, and `pnpm test`. This makes the exact source basis and configured command set explicit without asserting results."
},
{
"title": "Export a least-privilege diagnostics workflow and review it separately",
"benefit": "Add a workflow configuration that declares only `permissions: contents: read`, checks out the triggering commit, sets up Node 22 and pnpm 10.6.3, installs with `pnpm install --frozen-lockfile --ignore-scripts`, and invokes only `pnpm build`, `pnpm lint`, and `pnpm test`. Keep the workflow configuration review separate from any execution record: the supplied files contain no workflow evidence, so this requirement is presently unverified."
},
{
"title": "Prevent diagnostics from reaching release behavior",
"benefit": "Use explicit diagnostic script names rather than `pnpm release`. The existing release command includes `--push` and `npm publish`, whereas the three configured diagnostic scripts are limited to build, lint/format checking, and tests."
},
{
"title": "Make configuration evidence distinguishable from run evidence",
"benefit": "Document that manifest and workflow inspection establishes what is configured, while command output from a specific revision establishes what was executed. This avoids treating the presence of `test`, lockfile, or tooling dependencies as evidence of passing diagnostics."
}
]
}
},
{
"id": "design",
"dependsOn": [
"investigate"
],
"status": "completed",
"attempts": 1,
"maxAttempts": 2,
"output": {
"title": "Source-grounded diagnostics configuration for unjs/consola",
"rationale": "Inspected configuration basis: repository `unjs/consola` at commit `c47faac1738b7383971c6c20b5a34ffa15e7cc3b`; `package.json` identifies `pnpm@10.6.3`, and the committed `pnpm-lock.yaml` is present. The proposed diagnostics environment is Node 22 with the supplied immutable install command `pnpm install --frozen-lockfile --ignore-scripts`. A separately reviewable exported workflow should check out the selected revision, declare only `permissions: contents: read`, use that lockfile-based install, and invoke only the supported diagnostic scripts below. It must not invoke `release`, because that inspected script includes push and publish behavior. This is an inspection-derived configuration proposal, not an executed validation: no installation, workflow, build, lint, or test command was run, and no diagnostics are claimed to pass.",
"checks": [
{
"script": "build",
"purpose": "Runs the inspected `build` script, `unbuild`, to produce the package build artifacts from the source configuration. Operationally, this provides maintainers a repeatable build-stage signal for the selected revision without using release or publishing commands."
},
{
"script": "lint",
"purpose": "Runs the inspected `lint` script, `eslint . && prettier -c src examples test`, checking lint rules across the repository and formatting in `src`, `examples`, and `test`. Operationally, it provides a reviewable source-style and formatting check without modifying files, unlike `lint:fix`."
},
{
"script": "test",
"purpose": "Runs the inspected `test` script, `pnpm lint && pnpm vitest run --coverage`. It first performs the repository lint check, then runs Vitest with coverage enabled. Operationally, it provides the repository-defined test entry point and its configured coverage collection, while retaining the repository's own prerequisite lint behavior."
}
],
"limitations": [
"The configuration was inspected only. No dependency installation or `build`, `lint`, or `test` script was executed; there is no evidence that any diagnostic passes, that tests run, or that coverage is produced.",
"No existing workflow or diagnostics manifest was supplied. Therefore, an actual exported workflow\u2019s `contents: read` permission, checkout revision behavior, Node/pnpm setup, and frozen-lockfile installation remain unverified until its committed configuration is separately inspected.",
"The lockfile\u2019s presence at the specified commit is evidenced, but its full contents were omitted from the supplied evidence. Dependency resolution and lockfile/package-manifest consistency were not independently reviewed.",
"`test` already invokes `lint`; configuring both `lint` and `test` intentionally gives an independently visible lint check but duplicates lint work. Maintainers may retain that redundancy for clearer reporting or decide on a different reporting structure after review.",
"The diagnostics are limited to the supported names `build`, `lint`, and `test`. No claims are made about security scanning, dependency auditing, publishing readiness, coverage thresholds, runtime compatibility beyond unexecuted configuration compatibility, or external service reporting.",
"The inspected `release` script includes `changelogen --release --push` and `npm publish`; it is expressly excluded to preserve the authority boundary: read/configure an export only, with no publishing, deployment, spending authority, secrets use, or permission expansion."
]
}
},
{
"id": "build",
"dependsOn": [
"design"
],
"status": "completed",
"attempts": 1,
"maxAttempts": 2,
"output": {
"title": "Source-grounded diagnostics export for unjs/consola",
"summary": "Configured diagnostics: build, lint, and test, each matching an existing package script exactly once. Inspection basis: unjs/consola commit c47faac1738b7383971c6c20b5a34ffa15e7cc3b, package manager pnpm@10.6.3, Node 22, and the committed pnpm lockfile. Configuration evidence establishes the intended commands and environment only; repository diagnostics were not executed and are not claimed to pass. Exported diagnostics still need execution in the customer environment.",
"checkScripts": [
"build",
"lint",
"test"
],
"setupNotes": [
"Record the inspected source revision exactly as c47faac1738b7383971c6c20b5a34ffa15e7cc3b in the diagnostics manifest.",
"Use Node 22 and pnpm 10.6.3, matching the supplied repository profile and the package-manager declaration.",
"Use the committed pnpm lockfile with the supplied frozen, script-disabled install configuration to make dependency installation reproducible and to avoid lifecycle-script execution during installation.",
"Configure the exported workflow with only contents:read permission and ensure it runs against the selected committed revision.",
"Run only build, lint, and test. Do not invoke release: its inspected definition includes push and publish behavior.",
"The test script includes lint as its repository-defined prerequisite; retaining lint as a separate configured check provides separately visible lint reporting, while duplicating that work."
],
"extensionNotes": [
"Keep the diagnostics manifest and workflow review separate from execution evidence. A manifest or workflow proves configuration, not successful installation, build, linting, tests, or coverage generation.",
"For a future source revision, re-inspect the package manifest, package-manager version, lockfile presence, and the exact scripts before changing the configured check list.",
"Add new diagnostics only when they are established package-script names in the inspected manifest; do not infer checks from dependencies, documentation, or release tooling.",
"If reporting coverage, thresholds, security scans, or external-service uploads are later requested, review their configuration and permissions separately. None is evidenced or configured by this export.",
"Do not add publishing, deployment, secrets access, write permissions, or release commands to the diagnostics workflow.",
"Exported diagnostics still need execution in the customer environment; no result or passing status is represented here."
]
}
},
{
"id": "evaluate",
"dependsOn": [
"build"
],
"status": "completed",
"attempts": 1,
"maxAttempts": 2,
"output": {
"verdict": "pass",
"summary": "The exported diagnostics package satisfies all stated configuration and review acceptance criteria. This conclusion concerns static artifact inspection only; no repository installation, workflow, build, lint, or test execution occurred.",
"criteria": [
{
"criterion": "Every configured diagnostic exists in the inspected package.json.",
"passed": true,
"evidence": "`.starlight/diagnostics/manifest.json` configures `build`, `lint`, and `test`. At inspected revision `c47faac1738b7383971c6c20b5a34ffa15e7cc3b`, `package.json` defines those exact scripts with matching commands: `build: unbuild`, `lint: eslint . && prettier -c src examples test`, and `test: pnpm lint && pnpm vitest run --coverage`. The generated runner also rejects a check if its manifest command no longer matches `package.json`."
},
{
"criterion": "The manifest identifies the exact inspected source revision.",
"passed": true,
"evidence": "`.starlight/diagnostics/manifest.json` records `source.owner` as `unjs`, `source.name` as `consola`, and `source.commitSha` as `c47faac1738b7383971c6c20b5a34ffa15e7cc3b`, matching the supplied immutable repository evidence."
},
{
"criterion": "The exported workflow grants only contents:read and uses the committed lockfile.",
"passed": true,
"evidence": "`.github/workflows/starlight-diagnostics.yml` declares root-level `permissions: contents: read` with no additional permission entries. Its install step is `pnpm install --frozen-lockfile --ignore-scripts`; the inspected revision contains `pnpm-lock.yaml`, so this configuration requires the committed lockfile for installation. The workflow does not invoke the inspected `release` script."
},
{
"criterion": "The review distinguishes configuration evidence from unexecuted repository diagnostics.",
"passed": true,
"evidence": "The investigation, design, build summary, manifest `evaluationStatus`, and generated README consistently state that configuration establishes intended commands and environment only, and that installation, workflow execution, build, lint, test, and coverage results have not been established. No passing diagnostic result is asserted."
}
],
"limitations": [
"This review is limited to the supplied immutable repository evidence and exported artifacts; repository code, dependency installation, and workflow configuration were not executed.",
"`--frozen-lockfile` establishes the intended lockfile-based installation configuration, not proof that dependency resolution succeeds for this revision.",
"The workflow checks out the triggering GitHub ref rather than explicitly pinning `actions/checkout` to the manifest\u2019s recorded commit SHA. That does not contradict the stated acceptance criteria, but maintainers seeking an invariant revision-specific workflow should add an explicit checkout ref and independently review that change."
]
}
}
],
"artifacts": [
{
"id": "6be5f6bb-df11-4567-96f9-70665751af7a:.starlight/diagnostics/manifest.json",
"path": ".starlight/diagnostics/manifest.json",
"mediaType": "application/json",
"content": "{\n \"schemaVersion\": 1,\n \"source\": {\n \"owner\": \"unjs\",\n \"name\": \"consola\",\n \"commitSha\": \"c47faac1738b7383971c6c20b5a34ffa15e7cc3b\",\n \"inspectedAt\": \"2026-10-15T10:45:47.337Z\"\n },\n \"mission\": {\n \"ambition\": \"Make a useful, repeatable diagnostics system for this public Node repository.\",\n \"beneficiary\": \"Maintainers and contributors who need reviewable checks they can own and extend.\",\n \"outcome\": \"A source-grounded, runnable diagnostics package with a separate configuration review.\",\n \"acceptanceCriteria\": [\n \"Every configured diagnostic exists in the inspected package.json.\",\n \"The manifest identifies the exact inspected source revision.\",\n \"The exported workflow grants only contents:read and uses the committed lockfile.\",\n \"The review distinguishes configuration evidence from unexecuted repository diagnostics.\"\n ]\n },\n \"packageManager\": \"pnpm\",\n \"packageManagerVersion\": \"10.6.3\",\n \"nodeVersion\": \"22\",\n \"lockfile\": \"pnpm-lock.yaml\",\n \"installCommand\": [\n \"pnpm\",\n \"install\",\n \"--frozen-lockfile\",\n \"--ignore-scripts\"\n ],\n \"checks\": [\n {\n \"script\": \"build\",\n \"command\": \"unbuild\",\n \"purpose\": \"Runs the inspected `build` script, `unbuild`, to produce the package build artifacts from the source configuration. Operationally, this provides maintainers a repeatable build-stage signal for the selected revision without using release or publishing commands.\"\n },\n {\n \"script\": \"lint\",\n \"command\": \"eslint . && prettier -c src examples test\",\n \"purpose\": \"Runs the inspected `lint` script, `eslint . && prettier -c src examples test`, checking lint rules across the repository and formatting in `src`, `examples`, and `test`. Operationally, it provides a reviewable source-style and formatting check without modifying files, unlike `lint:fix`.\"\n },\n {\n \"script\": \"test\",\n \"command\": \"pnpm lint && pnpm vitest run --coverage\",\n \"purpose\": \"Runs the inspected `test` script, `pnpm lint && pnpm vitest run --coverage`. It first performs the repository lint check, then runs Vitest with coverage enabled. Operationally, it provides the repository-defined test entry point and its configured coverage collection, while retaining the repository's own prerequisite lint behavior.\"\n }\n ],\n \"permissions\": {\n \"repository\": \"contents:read\",\n \"externalWrites\": false,\n \"publish\": false\n },\n \"evaluationStatus\": \"Review the exported evaluation. CI diagnostics have not run until this workflow or runner is executed.\"\n}\n",
"sha256": "9082ca1e46c512af4d8d8167063373416d800390c4ae56719c82a1406e663168",
"createdBy": "compiler"
},
{
"id": "6be5f6bb-df11-4567-96f9-70665751af7a:.starlight/diagnostics/run.mjs",
"path": ".starlight/diagnostics/run.mjs",
"mediaType": "text/javascript",
"content": "#!/usr/bin/env node\n// Deterministic Starlight diagnostics runner v1. Generated configuration, never generated shell.\nimport { readFileSync, mkdirSync, writeFileSync } from 'node:fs';\nimport { spawnSync } from 'node:child_process';\nimport { fileURLToPath } from 'node:url';\nimport { resolve, dirname } from 'node:path';\nconst root = resolve(dirname(fileURLToPath(import.meta.url)), '../..');\nconst manifest = JSON.parse(readFileSync(resolve(root, '.starlight/diagnostics/manifest.json'), 'utf8'));\nconst pkg = JSON.parse(readFileSync(resolve(root, 'package.json'), 'utf8'));\nif (manifest.schemaVersion !== 1 || !['npm', 'pnpm', 'yarn'].includes(manifest.packageManager) || !Array.isArray(manifest.checks) || !manifest.checks.length) throw new Error('Invalid diagnostics manifest.');\nconst sourceObservedAt = new Date().toISOString();\nconst head = spawnSync('git', ['rev-parse', '--verify', 'HEAD'], { cwd: root, encoding: 'utf8', timeout: 5000, shell: false });\nconst candidateRevision = head.status === 0 ? head.stdout.trim() : '';\nconst observedSourceRevision = /^[a-f0-9]{40,64}$/i.test(candidateRevision) ? candidateRevision : null;\nconst tracked = observedSourceRevision ? spawnSync('git', ['status', '--porcelain', '--untracked-files=no'], { cwd: root, encoding: 'utf8', timeout: 5000, shell: false }) : null;\nconst trackedWorktreeDirty = tracked?.status === 0 ? Boolean(tracked.stdout.trim()) : null;\nconst inspectedSourceRevision = manifest.source.commitSha;\nconst sourceRevisionMatchesInspection = observedSourceRevision === null ? null : observedSourceRevision === inspectedSourceRevision;\nconst sourceState = observedSourceRevision === null || trackedWorktreeDirty === null ? 'unknown' : trackedWorktreeDirty ? 'dirty-worktree' : sourceRevisionMatchesInspection ? 'matching-clean' : 'different-commit';\nconst receipts = [];\nlet failed = false;\nfor (const check of manifest.checks) {\n if (!/^[A-Za-z0-9][A-Za-z0-9:_-]{0,99}$/.test(check.script) || typeof check.command !== 'string' || pkg.scripts?.[check.script] !== check.command) {\n receipts.push({ script: check.script, status: 'failed', reason: 'Package script changed or disappeared. Reinvestigate before running.' });\n failed = true;\n continue;\n }\n const start = Date.now();\n // The repository owner reviews and executes repository-supplied code in their own environment.\n const result = spawnSync(manifest.packageManager, ['run', check.script], { cwd: root, stdio: 'inherit', env: { ...process.env, CI: 'true' }, timeout: 300000, shell: false });\n const passed = result.status === 0 && !result.error;\n receipts.push({ script: check.script, command: check.command, status: passed ? 'passed' : 'failed', exitCode: result.status, durationMs: Date.now() - start, error: result.error?.message ?? null });\n if (!passed) failed = true;\n}\nconst report = { schemaVersion: 1, inspectedSourceRevision, observedSourceRevision, sourceRevisionMatchesInspection, trackedWorktreeDirty, sourceState, sourceObservedAt, observedAt: new Date().toISOString(), passed: !failed, checks: receipts };\nmkdirSync(resolve(root, '.starlight/diagnostics/results'), { recursive: true });\nwriteFileSync(resolve(root, '.starlight/diagnostics/results/latest.json'), JSON.stringify(report, null, 2) + '\\n');\nconsole.log(JSON.stringify(report, null, 2));\nprocess.exitCode = failed ? 1 : 0;\n",
"sha256": "7704fb9c8cbc24b05fa41a800a56616fb192d071740f731c7e8b7cf3a7b0bff1",
"createdBy": "compiler"
},
{
"id": "6be5f6bb-df11-4567-96f9-70665751af7a:.github/workflows/starlight-diagnostics.yml",
"path": ".github/workflows/starlight-diagnostics.yml",
"mediaType": "application/yaml",
"content": "# Starlight diagnostics v1. Review repository-supplied scripts before enabling.\nname: \"Source-grounded diagnostics export for unjs/consola\"\non:\n workflow_dispatch:\n pull_request:\npermissions:\n contents: read\nconcurrency:\n group: starlight-diagnostics-${{ github.ref }}\n cancel-in-progress: true\njobs:\n diagnostics:\n runs-on: ubuntu-latest\n timeout-minutes: 15\n steps:\n - uses: actions/checkout@v4\n with:\n persist-credentials: false\n - uses: actions/setup-node@v4\n with:\n node-version: \"22\"\n - name: Activate locked package manager\n run: |\n corepack enable\n corepack prepare pnpm@10.6.3 --activate\n - name: Install locked dependencies\n run: pnpm install --frozen-lockfile --ignore-scripts\n - name: Run source-derived diagnostics\n run: node .starlight/diagnostics/run.mjs\n",
"sha256": "006c71ffff478ccfc79ce911856ef4a01abe27c294958df9893d512c9e090dce",
"createdBy": "compiler"
},
{
"id": "6be5f6bb-df11-4567-96f9-70665751af7a:README.starlight-diagnostics.md",
"path": "README.starlight-diagnostics.md",
"mediaType": "text/markdown",
"content": "# Source-grounded diagnostics export for unjs/consola\n\nConfigured diagnostics: build, lint, and test, each matching an existing package script exactly once. Inspection basis: unjs/consola commit c47faac1738b7383971c6c20b5a34ffa15e7cc3b, package manager pnpm@10.6.3, Node 22, and the committed pnpm lockfile. Configuration evidence establishes the intended commands and environment only; repository diagnostics were not executed and are not claimed to pass. Exported diagnostics still need execution in the customer environment.\n\n## Mission\n\nMake a useful, repeatable diagnostics system for this public Node repository.\n\nBeneficiary: Maintainers and contributors who need reviewable checks they can own and extend.\n\nDesired outcome: A source-grounded, runnable diagnostics package with a separate configuration review.\n\n## Run locally\n\nSupported environments: Node 22 on Linux or macOS. Check out unjs/consola at c47faac1738b7383971c6c20b5a34ffa15e7cc3b, then copy these exported files into that repository. Review the selected package scripts before running repository-supplied code.\n\n```sh\ncorepack enable\ncorepack prepare pnpm@10.6.3 --activate\npnpm install --frozen-lockfile --ignore-scripts\nnode .starlight/diagnostics/run.mjs\n```\n\nThe runner checks each script against the inspected command, executes it with a five-minute timeout, records exit codes and writes .starlight/diagnostics/results/latest.json. A failing diagnostic returns a nonzero exit code. Installation uses --ignore-scripts or equivalent; projects requiring package lifecycle scripts need an owner-reviewed setup change.\n\nThe receipt distinguishes inspectedSourceRevision from observedSourceRevision (Git HEAD at run start, or null when unavailable), reports sourceRevisionMatchesInspection and trackedWorktreeDirty, and never substitutes the inspected SHA for an observed execution checkout. A different commit remains runnable so future pull requests can use the workflow. sourceState matching-clean means only a matching Git commit and no tracked-file changes at observation; it does not attest untracked files, installed dependencies or all executed bytes.\n\n## Selected diagnostics\n\n- build: Runs the inspected `build` script, `unbuild`, to produce the package build artifacts from the source configuration. Operationally, this provides maintainers a repeatable build-stage signal for the selected revision without using release or publishing commands.\n Command in the inspected repository: unbuild\n- lint: Runs the inspected `lint` script, `eslint . && prettier -c src examples test`, checking lint rules across the repository and formatting in `src`, `examples`, and `test`. Operationally, it provides a reviewable source-style and formatting check without modifying files, unlike `lint:fix`.\n Command in the inspected repository: eslint . && prettier -c src examples test\n- test: Runs the inspected `test` script, `pnpm lint && pnpm vitest run --coverage`. It first performs the repository lint check, then runs Vitest with coverage enabled. Operationally, it provides the repository-defined test entry point and its configured coverage collection, while retaining the repository's own prerequisite lint behavior.\n Command in the inspected repository: pnpm lint && pnpm vitest run --coverage\n\n## Evidence\n\n- [package.json](https://github.com/unjs/consola/blob/c47faac1738b7383971c6c20b5a34ffa15e7cc3b/package.json): The package manifest defines the three requested diagnostics: `build`, `lint`, and `test`. The test script invokes linting before running Vitest with coverage; none of these commands was executed in this review.\n- [package.json](https://github.com/unjs/consola/blob/c47faac1738b7383971c6c20b5a34ffa15e7cc3b/package.json): The manifest pins the package-manager identity and version to pnpm 10.6.3, providing a source-grounded value for diagnostics setup.\n- [package.json](https://github.com/unjs/consola/blob/c47faac1738b7383971c6c20b5a34ffa15e7cc3b/package.json): The package declares supported Node.js engine ranges. A Node 22 diagnostics environment is compatible with the declared `>=16.10.0` alternative, but compatibility was not exercised.\n- [pnpm-lock.yaml](https://github.com/unjs/consola/blob/c47faac1738b7383971c6c20b5a34ffa15e7cc3b/pnpm-lock.yaml): A committed pnpm lockfile is present in the inspected revision. Its contents were not available in the supplied evidence, so dependency resolution and lockfile consistency were not independently reviewed.\n- [package.json](https://github.com/unjs/consola/blob/c47faac1738b7383971c6c20b5a34ffa15e7cc3b/package.json): The manifest contains a release script with push and publish behavior. A diagnostics workflow should not invoke this script because it exceeds the mission's non-publishing and non-deployment constraints.\n- [README.md](https://github.com/unjs/consola/blob/c47faac1738b7383971c6c20b5a34ffa15e7cc3b/README.md): Coverage-reporting badge markup is commented out in the README. This is documentation configuration only and is not evidence that coverage reporting or upload is configured or has run.\n\n## Install the workflow\n\nThe export contains .github/workflows/starlight-diagnostics.yml. Review it, commit the files, then use its manual dispatch or open a pull request. Starlight has not committed, pushed, deployed or run this workflow. The workflow grants contents:read, disables persisted checkout credentials, does not reference secrets, and does not publish. Repository code and dependencies still run in the selected environment; this is not a sandbox guarantee. GitHub runners, model calls and dependency services may incur charges under your accounts.\n\n## Acceptance and limitations\n\n- Every configured diagnostic exists in the inspected package.json.\n- The manifest identifies the exact inspected source revision.\n- The exported workflow grants only contents:read and uses the committed lockfile.\n- The review distinguishes configuration evidence from unexecuted repository diagnostics.\n\n- The configuration was inspected only. No dependency installation or `build`, `lint`, or `test` script was executed; there is no evidence that any diagnostic passes, that tests run, or that coverage is produced.\n- No existing workflow or diagnostics manifest was supplied. Therefore, an actual exported workflow\u2019s `contents: read` permission, checkout revision behavior, Node/pnpm setup, and frozen-lockfile installation remain unverified until its committed configuration is separately inspected.\n- The lockfile\u2019s presence at the specified commit is evidenced, but its full contents were omitted from the supplied evidence. Dependency resolution and lockfile/package-manifest consistency were not independently reviewed.\n- `test` already invokes `lint`; configuring both `lint` and `test` intentionally gives an independently visible lint check but duplicates lint work. Maintainers may retain that redundancy for clearer reporting or decide on a different reporting structure after review.\n- The diagnostics are limited to the supported names `build`, `lint`, and `test`. No claims are made about security scanning, dependency auditing, publishing readiness, coverage thresholds, runtime compatibility beyond unexecuted configuration compatibility, or external service reporting.\n- The inspected `release` script includes `changelogen --release --push` and `npm publish`; it is expressly excluded to preserve the authority boundary: read/configure an export only, with no publishing, deployment, spending authority, secrets use, or permission expansion.\n\n- Record the inspected source revision exactly as c47faac1738b7383971c6c20b5a34ffa15e7cc3b in the diagnostics manifest.\n- Use Node 22 and pnpm 10.6.3, matching the supplied repository profile and the package-manager declaration.\n- Use the committed pnpm lockfile with the supplied frozen, script-disabled install configuration to make dependency installation reproducible and to avoid lifecycle-script execution during installation.\n- Configure the exported workflow with only contents:read permission and ensure it runs against the selected committed revision.\n- Run only build, lint, and test. Do not invoke release: its inspected definition includes push and publish behavior.\n- The test script includes lint as its repository-defined prerequisite; retaining lint as a separate configured check provides separately visible lint reporting, while duplicating that work.\n\nA generated configuration and a model evaluation do not establish that this repository passes diagnostics. Execute the runner and inspect its receipt before making that claim.\n\n## Extend\n\n- Keep the diagnostics manifest and workflow review separate from execution evidence. A manifest or workflow proves configuration, not successful installation, build, linting, tests, or coverage generation.\n- For a future source revision, re-inspect the package manifest, package-manager version, lockfile presence, and the exact scripts before changing the configured check list.\n- Add new diagnostics only when they are established package-script names in the inspected manifest; do not infer checks from dependencies, documentation, or release tooling.\n- If reporting coverage, thresholds, security scans, or external-service uploads are later requested, review their configuration and permissions separately. None is evidenced or configured by this export.\n- Do not add publishing, deployment, secrets access, write permissions, or release commands to the diagnostics workflow.\n- Exported diagnostics still need execution in the customer environment; no result or passing status is represented here.\n\nEdit mission configuration or add a supported package diagnostic, then reinvestigate. Keep the source revision, script command and receipt together. The versioned manifest is plain JSON; there is no Starlight runtime dependency or hosted account requirement.\n",
"sha256": "5fa886a1147ef6679eefb879cd59451fce1e964fb38b28ae59232a8eda31efe6",
"createdBy": "build"
},
{
"id": "6be5f6bb-df11-4567-96f9-70665751af7a:evaluation",
"path": ".starlight/diagnostics/evaluation.json",
"mediaType": "application/json",
"content": "{\n \"schemaVersion\": 1,\n \"modelReview\": {\n \"verdict\": \"pass\",\n \"summary\": \"The exported diagnostics package satisfies all stated configuration and review acceptance criteria. This conclusion concerns static artifact inspection only; no repository installation, workflow, build, lint, or test execution occurred.\",\n \"criteria\": [\n {\n \"criterion\": \"Every configured diagnostic exists in the inspected package.json.\",\n \"passed\": true,\n \"evidence\": \"`.starlight/diagnostics/manifest.json` configures `build`, `lint`, and `test`. At inspected revision `c47faac1738b7383971c6c20b5a34ffa15e7cc3b`, `package.json` defines those exact scripts with matching commands: `build: unbuild`, `lint: eslint . && prettier -c src examples test`, and `test: pnpm lint && pnpm vitest run --coverage`. The generated runner also rejects a check if its manifest command no longer matches `package.json`.\"\n },\n {\n \"criterion\": \"The manifest identifies the exact inspected source revision.\",\n \"passed\": true,\n \"evidence\": \"`.starlight/diagnostics/manifest.json` records `source.owner` as `unjs`, `source.name` as `consola`, and `source.commitSha` as `c47faac1738b7383971c6c20b5a34ffa15e7cc3b`, matching the supplied immutable repository evidence.\"\n },\n {\n \"criterion\": \"The exported workflow grants only contents:read and uses the committed lockfile.\",\n \"passed\": true,\n \"evidence\": \"`.github/workflows/starlight-diagnostics.yml` declares root-level `permissions: contents: read` with no additional permission entries. Its install step is `pnpm install --frozen-lockfile --ignore-scripts`; the inspected revision contains `pnpm-lock.yaml`, so this configuration requires the committed lockfile for installation. The workflow does not invoke the inspected `release` script.\"\n },\n {\n \"criterion\": \"The review distinguishes configuration evidence from unexecuted repository diagnostics.\",\n \"passed\": true,\n \"evidence\": \"The investigation, design, build summary, manifest `evaluationStatus`, and generated README consistently state that configuration establishes intended commands and environment only, and that installation, workflow execution, build, lint, test, and coverage results have not been established. No passing diagnostic result is asserted.\"\n }\n ],\n \"limitations\": [\n \"This review is limited to the supplied immutable repository evidence and exported artifacts; repository code, dependency installation, and workflow configuration were not executed.\",\n \"`--frozen-lockfile` establishes the intended lockfile-based installation configuration, not proof that dependency resolution succeeds for this revision.\",\n \"The workflow checks out the triggering GitHub ref rather than explicitly pinning `actions/checkout` to the manifest\\u2019s recorded commit SHA. That does not contradict the stated acceptance criteria, but maintainers seeking an invariant revision-specific workflow should add an explicit checkout ref and independently review that change.\"\n ]\n },\n \"deterministicChecks\": [\n {\n \"criterion\": \"Supported repository and reproducible install\",\n \"passed\": true,\n \"evidence\": \"pnpm-lock.yaml; pnpm install --frozen-lockfile --ignore-scripts\"\n },\n {\n \"criterion\": \"Every selected diagnostic exists in the inspected package.json\",\n \"passed\": true,\n \"evidence\": \"build: unbuild\\nlint: eslint . && prettier -c src examples test\\ntest: pnpm lint && pnpm vitest run --coverage\"\n },\n {\n \"criterion\": \"Builder configuration implements the architect plan\",\n \"passed\": true,\n \"evidence\": \"Selected: build, lint, test. Planned: build, lint, test.\"\n },\n {\n \"criterion\": \"Investigation excerpts match immutable repository evidence\",\n \"passed\": true,\n \"evidence\": \"package.json@c47faac1738b7383971c6c20b5a34ffa15e7cc3b\\npackage.json@c47faac1738b7383971c6c20b5a34ffa15e7cc3b\\npackage.json@c47faac1738b7383971c6c20b5a34ffa15e7cc3b\\npnpm-lock.yaml@c47faac1738b7383971c6c20b5a34ffa15e7cc3b\\npackage.json@c47faac1738b7383971c6c20b5a34ffa15e7cc3b\\nREADME.md@c47faac1738b7383971c6c20b5a34ffa15e7cc3b\"\n }\n ],\n \"executionProof\": \"Repository diagnostics have not been executed by this mission.\",\n \"historicalModelReviewSourceCommit\": \"01166b4fe3c57475b45c5d533b8cd8003758e602\",\n \"compilerRegeneration\": {\n \"kind\": \"deterministic-only\",\n \"reason\": \"Correct executed-source provenance; no new model calls. Historical model review did not inspect regenerated runner.\",\n \"independentReview\": \"See docs/frontier/acceptance.md and scripts/acceptance/frontier/provenance.mjs.\"\n }\n}\n",
"sha256": "b24476c6a3ef8023302c2281177343ac8b2f7c6f171efddad2e53ac2f33b00ee",
"createdBy": "evaluate"
}
],
"receipts": [
{
"id": "62c4c663-fc33-43fc-8efa-9f0e7cfbf377:model",
"taskId": "investigate",
"attempt": 1,
"kind": "model",
"operation": "structured_generation",
"status": "completed",
"startedAt": "2026-10-15T10:45:46.545Z",
"finishedAt": "2026-10-15T10:45:57.451Z",
"inputTokens": 4934,
"outputTokens": 1066,
"provider": "vercel-ai-gateway",
"model": "openai/gpt-5.6-terra",
"costUsdMicros": null
},
{
"id": "62c4c663-fc33-43fc-8efa-9f0e7cfbf377:repository",
"taskId": "investigate",
"attempt": 1,
"kind": "tool",
"operation": "github.readRepository",
"status": "completed",
"startedAt": "2026-10-15T10:45:46.545Z",
"finishedAt": "2026-10-15T10:45:47.339Z",
"sourceUrls": [
"https://github.com/unjs/consola/blob/c47faac1738b7383971c6c20b5a34ffa15e7cc3b/package.json",
"https://github.com/unjs/consola/blob/c47faac1738b7383971c6c20b5a34ffa15e7cc3b/pnpm-lock.yaml",
"https://github.com/unjs/consola/blob/c47faac1738b7383971c6c20b5a34ffa15e7cc3b/README.md"
]
},
{
"id": "83eccd53-0d12-4fba-b21e-036bed8d3864:model",
"taskId": "design",
"attempt": 1,
"kind": "model",
"operation": "structured_generation",
"status": "completed",
"startedAt": "2026-10-15T10:45:57.452Z",
"finishedAt": "2026-10-15T10:46:05.573Z",
"inputTokens": 5877,
"outputTokens": 694,
"provider": "vercel-ai-gateway",
"model": "openai/gpt-5.6-terra",
"costUsdMicros": null
},
{
"id": "49d32f13-b783-4cba-a608-fb44020c7fb7:model",
"taskId": "build",
"attempt": 1,
"kind": "model",
"operation": "structured_generation",
"status": "completed",
"startedAt": "2026-10-15T10:46:05.575Z",
"finishedAt": "2026-10-15T10:46:12.280Z",
"inputTokens": 6577,
"outputTokens": 587,
"provider": "vercel-ai-gateway",
"model": "openai/gpt-5.6-terra",
"costUsdMicros": null
},
{
"id": "88937e8c-64ed-41d2-a7c7-592a69283e34:model",
"taskId": "evaluate",
"attempt": 1,
"kind": "model",
"operation": "structured_generation",
"status": "completed",
"startedAt": "2026-10-15T10:46:12.282Z",
"finishedAt": "2026-10-15T10:46:20.279Z",
"inputTokens": 11389,
"outputTokens": 800,
"provider": "vercel-ai-gateway",
"model": "openai/gpt-5.6-terra",
"costUsdMicros": null
}
],
"usage": {
"modelCalls": 4,
"toolCalls": 1,
"inputTokens": 28777,
"outputTokens": 3147,
"costUsdMicros": null,
"unsettledAttempts": 0
},
"createdAt": "2026-10-15T10:45:46.543Z",
"updatedAt": "2026-10-15T10:46:20.279Z",
"repository": {
"owner": "unjs",
"name": "consola",
"commitSha": "c47faac1738b7383971c6c20b5a34ffa15e7cc3b",
"defaultBranch": "main",
"fetchedAt": "2026-10-15T10:45:47.337Z",
"files": [
{
"path": "package.json",
"content": "{\n \"name\": \"consola\",\n \"version\": \"3.4.2\",\n \"description\": \"Elegant Console Wrapper\",\n \"keywords\": [\n \"console\",\n \"logger\",\n \"reporter\",\n \"elegant\",\n \"cli\",\n \"universal\",\n \"unified\",\n \"prompt\",\n \"clack\",\n \"format\",\n \"error\",\n \"stacktrace\"\n ],\n \"repository\": \"unjs/consola\",\n \"license\": \"MIT\",\n \"type\": \"module\",\n \"exports\": {\n \".\": {\n \"node\": {\n \"import\": {\n \"types\": \"./dist/index.d.mts\",\n \"default\": \"./dist/index.mjs\"\n },\n \"require\": {\n \"types\": \"./dist/index.d.cts\",\n \"default\": \"./lib/index.cjs\"\n }\n },\n \"default\": {\n \"import\": {\n \"types\": \"./dist/browser.d.mts\",\n \"default\": \"./dist/browser.mjs\"\n },\n \"require\": {\n \"types\": \"./dist/browser.d.cts\",\n \"default\": \"./dist/browser.cjs\"\n }\n }\n },\n \"./browser\": {\n \"import\": {\n \"types\": \"./dist/browser.d.mts\",\n \"default\": \"./dist/browser.mjs\"\n },\n \"require\": {\n \"types\": \"./dist/browser.d.cts\",\n \"default\": \"./dist/browser.cjs\"\n }\n },\n \"./basic\": {\n \"node\": {\n \"import\": {\n \"types\": \"./dist/basic.d.mts\",\n \"default\": \"./dist/basic.mjs\"\n },\n \"require\": {\n \"types\": \"./dist/basic.d.cts\",\n \"default\": \"./dist/basic.cjs\"\n }\n },\n \"default\": {\n \"import\": {\n \"types\": \"./dist/browser.d.mts\",\n \"default\": \"./dist/browser.mjs\"\n },\n \"require\": {\n \"types\": \"./dist/browser.d.cts\",\n \"default\": \"./dist/browser.cjs\"\n }\n }\n },\n \"./core\": {\n \"import\": {\n \"types\": \"./dist/core.d.mts\",\n \"default\": \"./dist/core.mjs\"\n },\n \"require\": {\n \"types\": \"./dist/core.d.cts\",\n \"default\": \"./dist/core.cjs\"\n }\n },\n \"./utils\": {\n \"import\": {\n \"types\": \"./dist/utils.d.mts\",\n \"default\": \"./dist/utils.mjs\"\n },\n \"require\": {\n \"types\": \"./dist/utils.d.cts\",\n \"default\": \"./dist/utils.cjs\"\n }\n }\n },\n \"main\": \"./lib/index.cjs\",\n \"module\": \"./dist/index.mjs\",\n \"browser\": \"./dist/browser.mjs\",\n \"types\": \"./dist/index.d.ts\",\n \"files\": [\n \"dist\",\n \"lib\",\n \"*.d.ts\"\n ],\n \"scripts\": {\n \"build\": \"unbuild\",\n \"dev\": \"vitest\",\n \"lint\": \"eslint . && prettier -c src examples test\",\n \"lint:fix\": \"eslint . --fix && prettier -w src examples test\",\n \"release\": \"pnpm test && pnpm build && changelogen --release --push && npm publish\",\n \"test\": \"pnpm lint && pnpm vitest run --coverage\"\n },\n \"devDependencies\": {\n \"@clack/prompts\": \"^0.10.0\",\n \"@types/node\": \"^22.13.10\",\n \"@vitest/coverage-v8\": \"^3.0.9\",\n \"changelogen\": \"^0.6.1\",\n \"defu\": \"^6.1.4\",\n \"eslint\": \"^9.22.0\",\n \"eslint-config-unjs\": \"^0.4.2\",\n \"is-unicode-supported\": \"^2.1.0\",\n \"prettier\": \"^3.5.3\",\n \"sentencer\": \"^0.2.1\",\n \"std-env\": \"^3.8.1\",\n \"string-width\": \"^7.2.0\",\n \"typescript\": \"^5.8.2\",\n \"unbuild\": \"^3.5.0\",\n \"vitest\": \"^3.0.9\"\n },\n \"engines\": {\n \"node\": \"^14.18.0 || >=16.10.0\"\n },\n \"packageManager\": \"pnpm@10.6.3\"\n}\n",
"sha": "77530691c7ffb888ceab4c3e9082d640cb391e6a",
"url": "https://github.com/unjs/consola/blob/c47faac1738b7383971c6c20b5a34ffa15e7cc3b/package.json"
},
{
"path": "pnpm-lock.yaml",
"content": "[Lockfile verified at immutable revision; 138945 bytes. Contents omitted by the evidence size limit.]",
"sha": "55f976a4fa4b0cefda9cf27e20063279fdabef57",
"url": "https://github.com/unjs/consola/blob/c47faac1738b7383971c6c20b5a34ffa15e7cc3b/pnpm-lock.yaml"
},
{
"path": "README.md",
"content": "# \ud83d\udc28 Consola\n\n> Elegant Console Wrapper\n\n[![npm version][npm-version-src]][npm-version-href]\n[![npm downloads][npm-downloads-src]][npm-downloads-href]\n[![bundle][bundle-src]][bundle-href]\n\n\n\n## Why Consola?\n\n\ud83d\udc4c Easy to use
\n\ud83d\udc85 Fancy output with fallback for minimal environments
\n\ud83d\udd0c Pluggable reporters
\n\ud83d\udcbb Consistent command line interface (CLI) experience
\n\ud83c\udff7 Tag support
\n\ud83d\ude8f Redirect `console` and `stdout/stderr` to consola and easily restore redirect.
\n\ud83c\udf10 Browser support
\n\u23ef Pause/Resume support
\n\ud83d\udc7b Mocking support
\n\ud83d\udc6e\u200d\u2642\ufe0f Spam prevention by throttling logs
\n\u276f Interactive prompt support powered by [`clack`](https://github.com/natemoo-re/clack)
\n\n## Installation\n\nUsing npm:\n\n```bash\nnpm i consola\n```\n\nUsing yarn:\n\n```bash\nyarn add consola\n```\n\nUsing pnpm:\n\n```bash\npnpm i consola\n```\n\n## Getting Started\n\n```js\n// ESM\nimport { consola, createConsola } from \"consola\";\n\n// CommonJS\nconst { consola, createConsola } = require(\"consola\");\n\nconsola.info(\"Using consola 3.0.0\");\nconsola.start(\"Building project...\");\nconsola.warn(\"A new version of consola is available: 3.0.1\");\nconsola.success(\"Project built!\");\nconsola.error(new Error(\"This is an example error. Everything is fine!\"));\nconsola.box(\"I am a simple box\");\nawait consola.prompt(\"Deploy to the production?\", {\n type: \"confirm\",\n});\n```\n\nWill display in the terminal:\n\n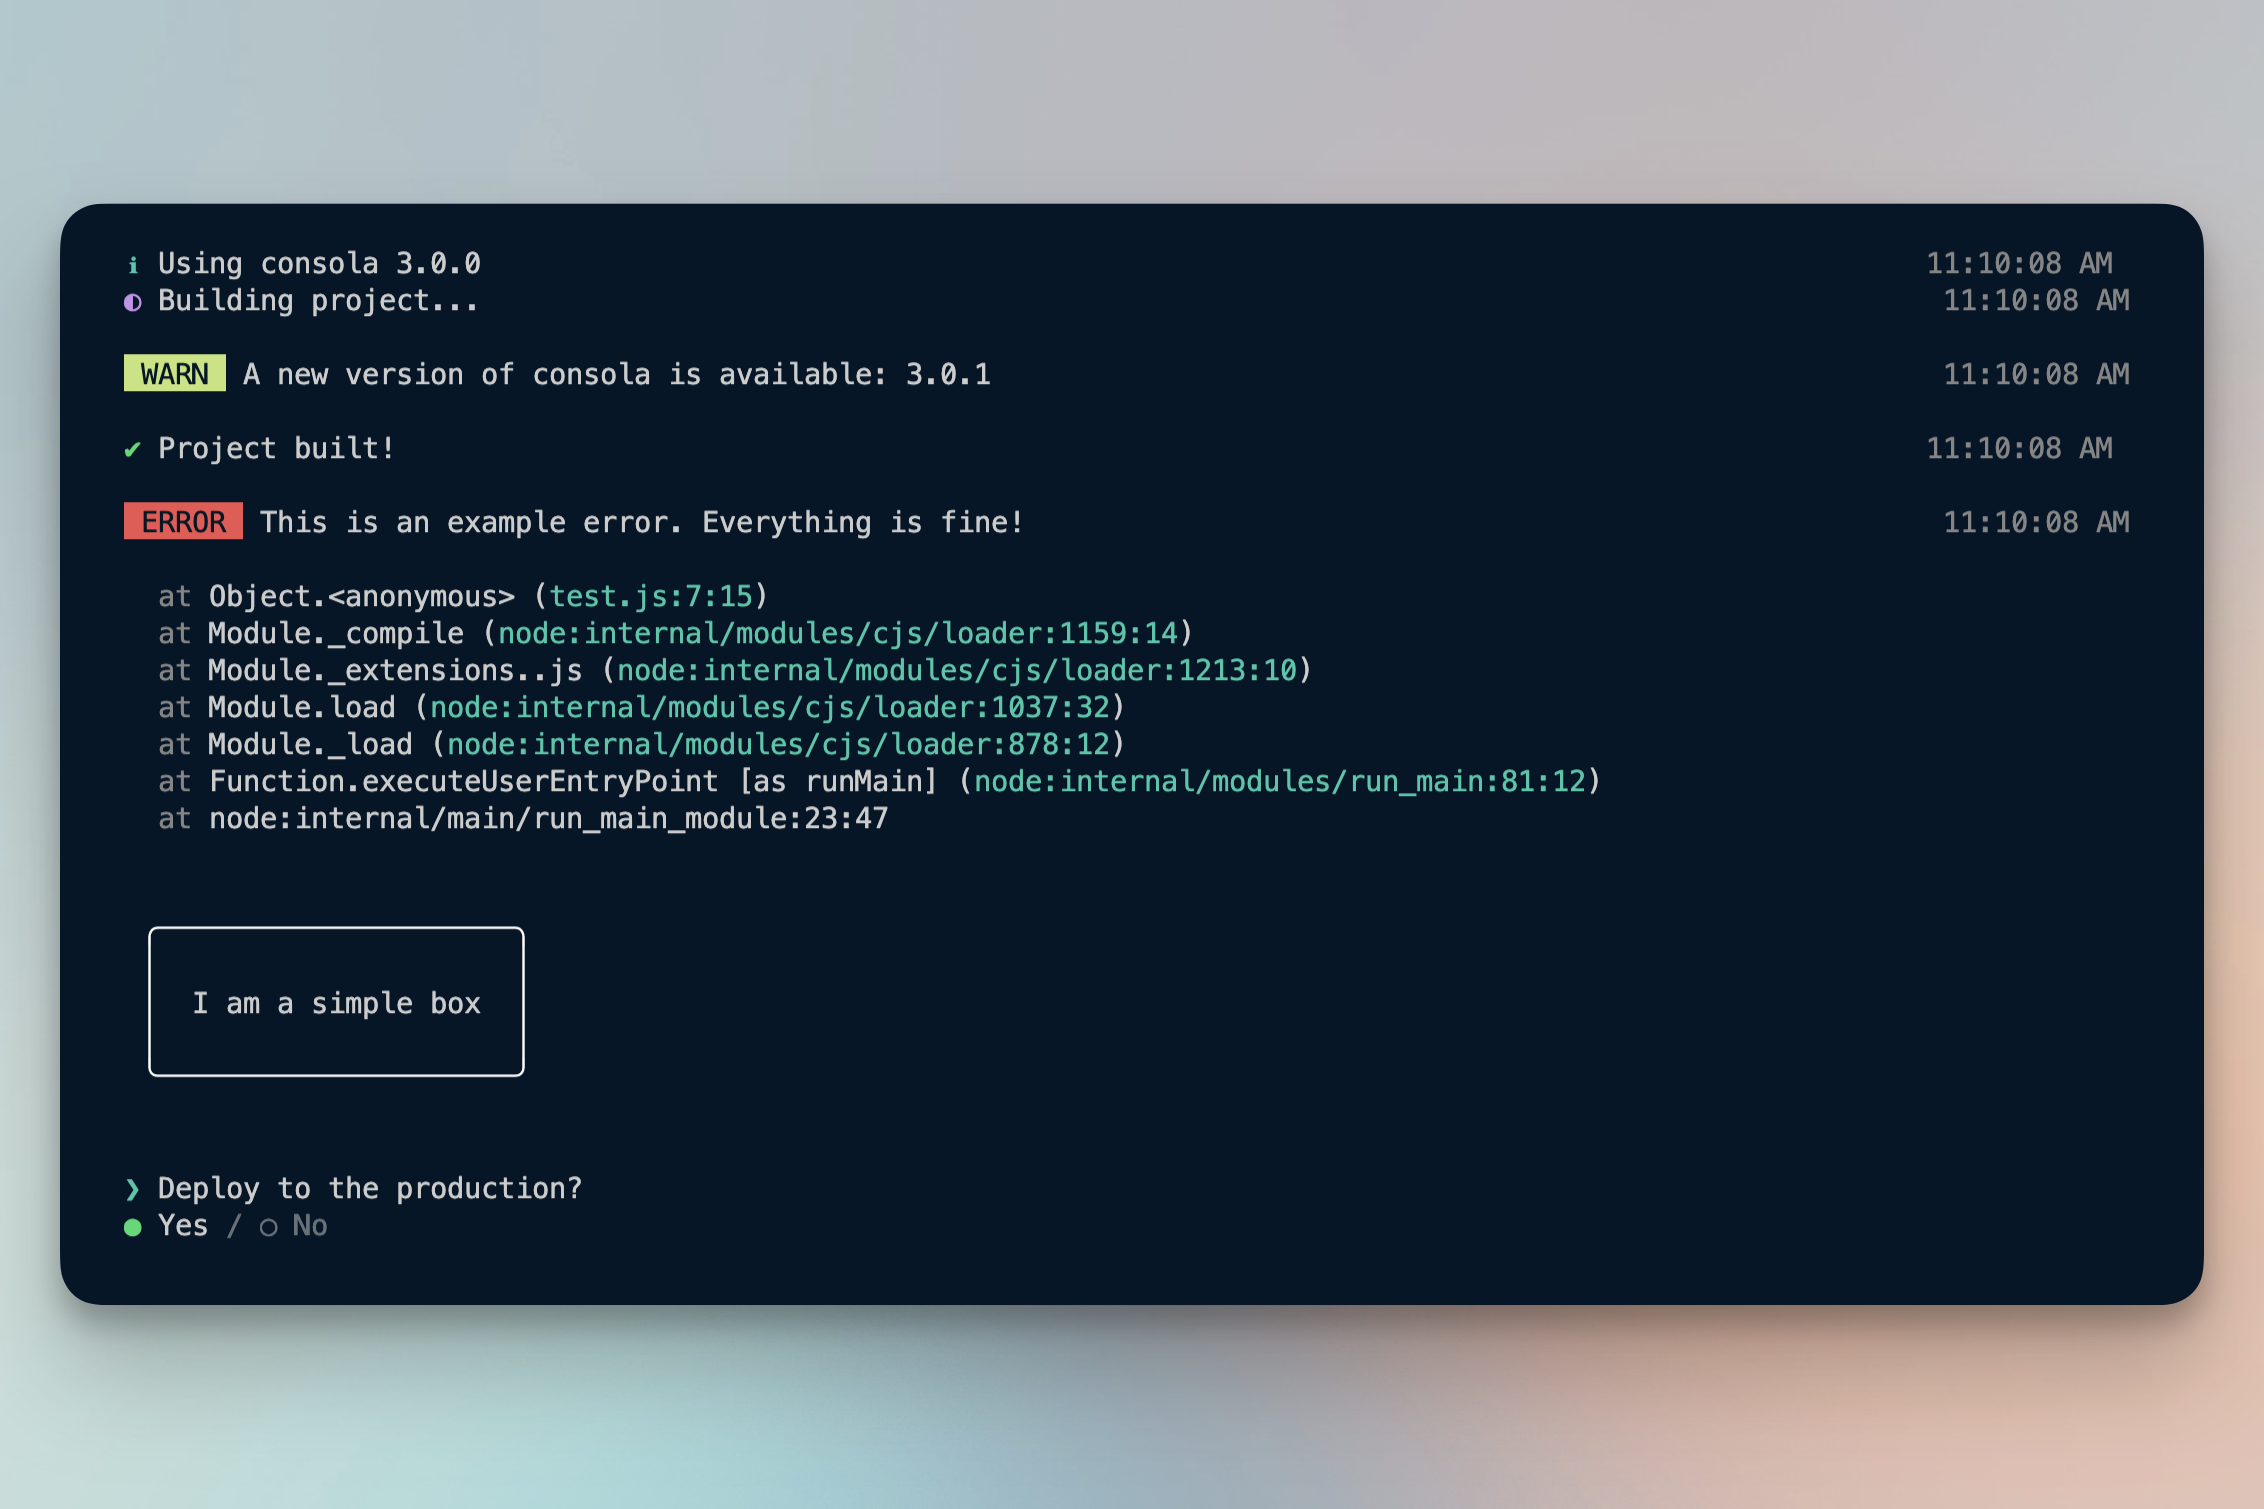\n\nYou can use smaller core builds without fancy reporter to save 80% of the bundle size:\n\n```ts\nimport { consola, createConsola } from \"consola/basic\";\nimport { consola, createConsola } from \"consola/browser\";\nimport { createConsola } from \"consola/core\";\n```\n\n## Consola Methods\n\n#### `(logObject)` `(args...)`\n\nLog to all reporters.\n\nExample: `consola.info('Message')`\n\n#### `await prompt(message, { type, cancel })`\n\nShow an input prompt. Type can either of `text`, `confirm`, `select` or `multiselect`.\n\nIf prompt is canceled by user (with Ctrol+C), default value will be resolved by default. This strategy can be configured by setting `{ cancel: \"...\" }` option:\n\n- `\"default\"` - Resolve the promise with the `default` value or `initial` value.\n- `\"undefined`\" - Resolve the promise with `undefined`.\n- `\"null\"` - Resolve the promise with `null`.\n- `\"symbol\"` - Resolve the promise with a symbol `Symbol.for(\"cancel\")`.\n- `\"reject\"` - Reject the promise with an error.\n\nSee [examples/prompt.ts](./examples/prompt.ts) for usage examples.\n\n#### `addReporter(reporter)`\n\n- Aliases: `add`\n\nRegister a custom reporter instance.\n\n#### `removeReporter(reporter?)`\n\n- Aliases: `remove`, `clear`\n\nRemove a registered reporter.\n\nIf no arguments are passed all reporters will be removed.\n\n#### `setReporters(reporter|reporter[])`\n\nReplace all reporters.\n\n#### `create(options)`\n\nCreate a new `Consola` instance and inherit all parent options for defaults.\n\n#### `withDefaults(defaults)`\n\nCreate a new `Consola` instance with provided defaults\n\n#### `withTag(tag)`\n\n- Aliases: `withScope`\n\nCreate a new `Consola` instance with that tag.\n\n#### `wrapConsole()` `restoreConsole()`\n\nGlobally redirect all `console.log`, etc calls to consola handlers.\n\n#### `wrapStd()` `restoreStd()`\n\nGlobally redirect all stdout/stderr outputs to consola.\n\n#### `wrapAll()` `restoreAll()`\n\nWrap both, std and console.\n\nconsole uses std in the underlying so calling `wrapStd` redirects console too.\nBenefit of this function is that things like `console.info` will be correctly redirected to the corresponding type.\n\n#### `pauseLogs()` `resumeLogs()`\n\n- Aliases: `pause`/`resume`\n\n**Globally** pause and resume logs.\n\nConsola will enqueue all logs when paused and then sends them to the reported when resumed.\n\n#### `mockTypes`\n\n- Aliases: `mock`\n\nMock all types. Useful for using with tests.\n\nThe first argument passed to `mockTypes` should be a callback function accepting `(typeName, type)` and returning the mocked value:\n\n```js\n// Jest\nconsola.mockTypes((typeName, type) => jest.fn());\n// Vitest\nconsola.mockTypes((typeName, type) => vi.fn());\n```\n\nPlease note that with the example above, everything is mocked independently for each type. If you need one mocked fn create it outside:\n\n```js\n// Jest\nconst fn = jest.fn();\n// Vitest\nconst fn = vi.fn();\nconsola.mockTypes(() => fn);\n```\n\nIf callback function returns a _falsy_ value, that type won't be mocked.\n\nFor example if you just need to mock `consola.fatal`:\n\n```js\n// Jest\nconsola.mockTypes((typeName) => typeName === \"fatal\" && jest.fn());\n// Vitest\nconsola.mockTypes((typeName) => typeName === \"fatal\" && vi.fn());\n```\n\n**NOTE:** Any instance of consola that inherits the mocked instance, will apply provided callback again.\nThis way, mocking works for `withTag` scoped loggers without need to extra efforts.\n\n## Custom Reporters\n\nConsola ships with 3 built-in reporters out of the box. A fancy colored reporter by default and fallsback to a basic reporter if running in a testing or CI environment detected using [unjs/std-env](https://github.com/unjs/std-env) and a basic browser reporter.\n\nYou can create a new reporter object that implements `{ log(logObject): () => { } }` interface.\n\n**Example:** Simple JSON reporter\n\n```ts\nimport { createConsola } from \"consola\";\n\nconst consola = createConsola({\n reporters: [\n {\n log: (logObj) => {\n console.log(JSON.stringify(logObj));\n },\n },\n ],\n});\n\n// Prints {\"date\":\"2023-04-18T12:43:38.693Z\",\"args\":[\"foo bar\"],\"type\":\"log\",\"level\":2,\"tag\":\"\"}\nconsola.log(\"foo bar\");\n```\n\n**Example:** Exit on fatal errors\n\n```ts\nimport { consola } from 'consola';\n\nconsola.addReporter({\n log(logObj) {\n if(logObj.type === 'fatal') {\n process.exit(1)\n }\n }\n})\n\n// Will exit on this line.\nconsola.fatal(\"fatal error\");\n```\n\n## Log Level\n\nConsola only shows logs with configured log level or below. (Default is `3`)\n\nAvailable log levels:\n\n- `0`: Fatal and Error\n- `1`: Warnings\n- `2`: Normal logs\n- `3`: Informational logs, success, fail, ready, start, ...\n- `4`: Debug logs\n- `5`: Trace logs\n- `-999`: Silent\n- `+999`: Verbose logs\n\nYou can set the log level by either:\n\n- Passing `level` option to `createConsola`\n- Setting `consola.level` on instance\n- Using the `CONSOLA_LEVEL` environment variable (not supported for browser and core builds).\n\n## Log Types\n\nLog types are exposed as `consola.[type](...)` and each is a preset of styles and log level.\n\nA list of all available built-in types is [available here](./src/constants.ts).\n\n## Creating a new instance\n\nConsola has a global instance and is recommended to use everywhere.\nIn case more control is needed, create a new instance.\n\n```js\nimport { createConsola } from \"consola\";\n\nconst logger = createConsola({\n // level: 4,\n // fancy: true | false\n // formatOptions: {\n // columns: 80,\n // colors: false,\n // compact: false,\n // date: false,\n // },\n});\n```\n\n## Integrations\n\n### With jest or vitest\n\n```js\ndescribe(\"your-consola-mock-test\", () => {\n beforeAll(() => {\n // Redirect std and console to consola too\n // Calling this once is sufficient\n consola.wrapAll();\n });\n\n beforeEach(() => {\n // Re-mock consola before each test call to remove\n // calls from before\n // Jest\n consola.mockTypes(() => jest.fn());\n // Vitest\n consola.mockTypes(() => vi.fn());\n });\n\n test(\"your test\", async () => {\n // Some code here\n\n // Let's retrieve all messages of `consola.log`\n // Get the mock and map all calls to their first argument\n const consolaMessages = consola.log.mock.calls.map((c) => c[0]);\n expect(consolaMessages).toContain(\"your message\");\n });\n});\n```\n\n### With jsdom\n\n```js\n{\n new jsdom.VirtualConsole().sendTo(consola);\n}\n```\n\n## Console Utils\n\n```ts\n// ESM\nimport {\n stripAnsi,\n centerAlign,\n rightAlign,\n leftAlign,\n align,\n box,\n colors,\n getColor,\n colorize,\n} from \"consola/utils\";\n\n// CommonJS\nconst { stripAnsi } = require(\"consola/utils\");\n```\n\n## Raw logging methods\n\nObjects sent to the reporter could lead to unexpected output when object is close to internal object structure containing either `message` or `args` props. To enforce the object to be interpreted as pure object, you can use the `raw` method chained to any log type.\n\n**Example:**\n\n```js\n// Prints \"hello\"\nconsola.log({ message: \"hello\" });\n\n// Prints \"{ message: 'hello' }\"\nconsola.log.raw({ message: \"hello\" });\n```\n\n## License\n\nMIT\n\n\n\n[npm-version-src]: https://img.shields.io/npm/v/consola?style=flat&colorA=18181B&colorB=F0DB4F\n[npm-version-href]: https://npmjs.com/package/consola\n[npm-downloads-src]: https://img.shields.io/npm/dm/consola?style=flat&colorA=18181B&colorB=F0DB4F\n[npm-downloads-href]: https://npmjs.com/package/consola\n[codecov-src]: https://img.shields.io/codecov/c/gh/unjs/consola/main?style=flat&colorA=18181B&colorB=F0DB4F\n[codecov-href]: https://codecov.io/gh/unjs/consola\n[bundle-src]: https://img.shields.io/bundlephobia/min/consola?style=flat&colorA=18181B&colorB=F0DB4F\n[bundle-href]: https://bundlephobia.com/result?p=consola\n",
"sha": "0486be92dc4e26ff3e633d62cd6d7913f31d462a",
"url": "https://github.com/unjs/consola/blob/c47faac1738b7383971c6c20b5a34ffa15e7cc3b/README.md"
}
]
},
"verification": [
{
"criterion": "Supported repository and reproducible install",
"passed": true,
"evidence": "pnpm-lock.yaml; pnpm install --frozen-lockfile --ignore-scripts"
},
{
"criterion": "Every selected diagnostic exists in the inspected package.json",
"passed": true,
"evidence": "build: unbuild\nlint: eslint . && prettier -c src examples test\ntest: pnpm lint && pnpm vitest run --coverage"
},
{
"criterion": "Builder configuration implements the architect plan",
"passed": true,
"evidence": "Selected: build, lint, test. Planned: build, lint, test."
},
{
"criterion": "Investigation excerpts match immutable repository evidence",
"passed": true,
"evidence": "package.json@c47faac1738b7383971c6c20b5a34ffa15e7cc3b\npackage.json@c47faac1738b7383971c6c20b5a34ffa15e7cc3b\npackage.json@c47faac1738b7383971c6c20b5a34ffa15e7cc3b\npnpm-lock.yaml@c47faac1738b7383971c6c20b5a34ffa15e7cc3b\npackage.json@c47faac1738b7383971c6c20b5a34ffa15e7cc3b\nREADME.md@c47faac1738b7383971c6c20b5a34ffa15e7cc3b"
}
]
}
}